

How does the attack work? #
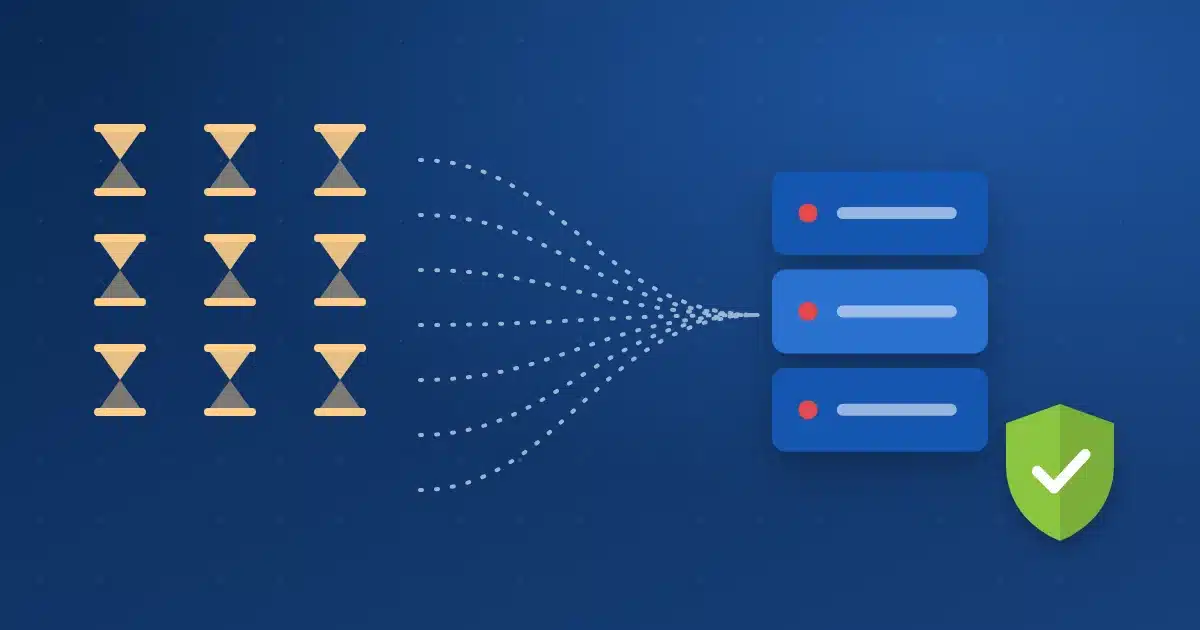
When someone visits your site, their browser sends a complete HTTP request in a fraction of a second. In Slowloris the attacker sends only the start of the request, then one small extra line every 10 or 15 seconds, so the request never completes. The server assumes a slow visitor and keeps the connection open, waiting.
- The attacker opens hundreds of connections: Sometimes from a single machine, with very little bandwidth.
- Keeps them alive slowly: Each connection sends a small piece just before the server’s timeout.
- The server runs out of connections: Web servers that reserve a process per connection hit their limit.
- Real visitors are turned away: The site looks down while CPU and bandwidth stay almost idle.
Signs of the attack #
- The site does not respond, yet CPU and memory usage are not high.
- Many open connections from a small number of addresses.
- Web server logs show incomplete or timed-out requests.
How to protect your server #
| Method | What it does |
|---|---|
| Per-address connection limit | The firewall (such as CSF) stops one address from opening many connections at the same time. |
| Short request timeout | In Apache, mod_reqtimeout sets the maximum time for a full request to arrive, closing slow connections. |
| Event-based web server | LiteSpeed and Nginx do not reserve a full process per connection, so they withstand this attack much better. |
| Cloud protection in front | Cloudflare accepts connections instead of your server and passes only complete requests. Read Under Attack mode. |
How Hyyat Host protects your site #
- WordPress hosting servers run LiteSpeed, and the CSF firewall limits connections per address.
- Imunify360 watches for suspicious requests and blocks their sources.
- You can connect your site to Cloudflare for an extra layer of protection.
For private servers, we configure these protections as part of our server management service. Learn more about Hyyat Host DoS protection.
Frequently asked questions #
How is Slowloris different from a regular DDoS attack?
A regular DDoS floods the server with huge volumes of traffic or requests. Slowloris uses few, very slow connections, so it is hard to spot from usage alone.
Is a site on shared hosting affected?
Protection is the server’s job, and it is configured on our servers, so you need no setup in your site.
Is Cloudflare enough on its own?
It protects your site as long as visitors pass through it. If your server’s real IP is known, attackers can bypass it, so server protection is still needed.


